Your Microsoft 365 Security, Held to One Standard Every Month
Every Microsoft 365 tenant Ceifa manages runs on the same security baseline: our tested settings for sign-in, email, sharing, devices and apps. We apply it when you join and keep checking it after. When a setting moves, we put it back or record why it stays, and you see it all in your monthly security report.
What the Ceifa Baseline Covers in Your Tenant
These are the settings we hold every managed tenant to, and the routine that keeps them in place after onboarding is finished.
The Ceifa baseline, area by area
Same in every managed tenantSign-in and Admin Accounts
MFA for every user, legacy sign-in methods blocked, conditional access for risky sign-ins, and as few global admins as your organization can work with. Account takeover is the most common way into a tenant, so this area goes in first.
Email Protection
Anti-phishing and anti-spam policies, a warning banner on messages from outside, and automatic forwarding to external addresses turned off unless there is an agreed business reason for it.
Sharing in SharePoint, OneDrive and Teams
Guest access and "anyone with the link" sharing are set to what your organization actually needs, with links that expire, so company files do not quietly end up in places nobody intended.
Devices and Third-Party Apps
Intune device compliance is tied to sign-in, users cannot grant third-party apps access to company data on their own, and add-ins are reviewed before they are allowed.
Drift Checks
Automated checks compare each tenant with the baseline. When a setting has moved, whether from an admin shortcut, a new Microsoft default or a temporary fix that was never undone, it becomes a ticket for our team to reverse or document.
Monthly Security Report
Each month you see which settings match the baseline, what drifted and what we did about it, plus any open risks. It is a ready answer when an insurer or a client sends you a security questionnaire.
One Owner for the Standard, a Whole Team to Enforce It
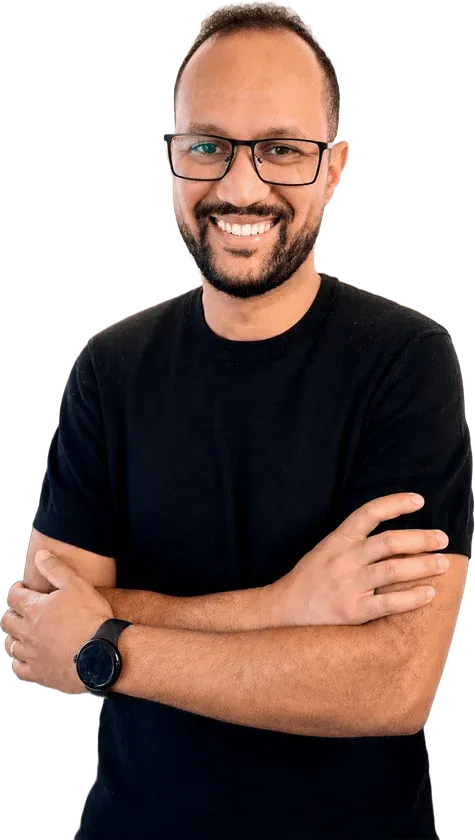
The Ceifa baseline is maintained by Helio Pereira, Senior Solutions Architect. Helio decides which settings belong in it, updates it when Microsoft changes the platform, and signs off any exception a client needs so it is recorded instead of forgotten. Our service desk then applies and enforces that same standard in every tenant we manage, yours included.
What Happens After You Join Ceifa
The first four steps happen during onboarding. The last two repeat every month for as long as we run your IT. Ceifa is a Microsoft Solutions Partner for Modern Work.
See Where You Stand
During onboarding we compare your tenant with the Ceifa baseline and list every difference, grouped by sign-in, email, sharing, devices and apps.
Agree the Exceptions
Some settings need to work differently for how your organization operates. We agree those with you and write down the reason, so every exception is a decision rather than an accident.
Apply the Baseline
Changes go in by risk, sign-in and admin accounts first. Where staff will notice something new, such as an MFA prompt, we tell them before it happens.
Record the Starting Point
At the end of onboarding you get a written record of how your tenant is configured. Every later report is measured against it.
Watch for Drift
OngoingAutomated checks keep comparing your live settings with the baseline. Anything that has moved raises a ticket with our service desk instead of waiting for someone to stumble on it.
Fix It and Report It
OngoingDrift is reversed or documented as an approved exception, and your monthly security report shows what changed and how it was handled. This continues for as long as Ceifa manages your IT.
Questions Clients Ask Us
See How Your Tenant Measures Up
Book a call and we will walk through how your Microsoft 365 settings compare with the baseline we run for every managed client, and what keeping it there each month would involve.
Burnaby Head Office: 3999 Henning Dr #402, Burnaby, BC V5C 6P7 | Victoria Office: 300-848 Courtney Street, Victoria, BC V8W 1C4